A Cybersecurity Guide for College Students: Safeguarding Your Personal Information

In a world where so much of our lives happens online, keeping up with your cybersecurity is more important than ever.
One of the most common cybersecurity threats is phishing, where scammers trick you into revealing your personal information. To help you navigate these risks, we’ve compiled some essential tips and information on recognizing and avoiding phishing and other scams.
What's Phishing and How Do I Protect Myself?
Phishing is an online scam where attackers pose as a trusted source through emails, aiming to get you to share personal information. Their methods can be very convincing, leading you to unknowingly reveal sensitive details like passwords, personal info, or credit card numbers. Usually these phishing attempts will try to instill a sense of urgency in you in order to get you to click a link or download an attachment.
At first glance phishing scams can seem very real but there are clues like unusual email addresses, poor grammar, or suspicious link that you can watch out before falling victim. To protect yourself from a phishing attack stay cautious and follow these tips:
- Verify the Sender: Always check the sender’s email address. Scammers frequently use addresses that closely resemble real ones to trick you.
- Look for Red Flags: Be cautious of emails that create a sense of urgency, ask for personal information, or contain suspicious links.
- Don’t Click on Unknown Links: Instead of hovering or hard pressing the link on a mobile device, copy the link and paste it into a note or a text editor to see the actual URL. If it looks suspicious, don't click.
- Keep Your Device Software Up to Date: Ensure that your operating system, browser, and security software are up to date across all devices, including Macs, PCs, and mobile devices.
Guarding Against Suspicious Emails & Weak Passwords
What to Do If You Receive a Suspicious Email
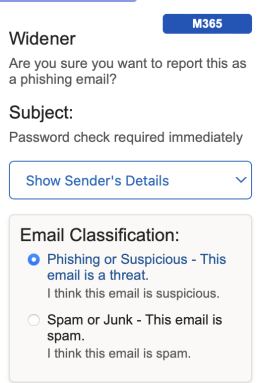
At some point, you’re bound to encounter a suspicious email that raises your eyebrows. When that day arrives, you’ll be prepared to tackle it head-on with confidence. Follow these key steps to navigate the situation effectively:
- Don’t Respond: Never reply to the email or provide personal information.
- Verify the Source: Contact the supposed sender through a known, trusted method (e.g., their official website or phone number) to confirm the email’s authenticity.
- Report It: Use the phish alert button or forward it to phish@widener.edu.
- Delete or Block: Delete the email and block the sender to prevent future messages.
Creating Strong Passwords
Our password acts as the first line of defense against unauthorized access, making it crucial to ensure it is both complex and unique. By investing your time in developing unique and strong passwords, you significantly reduce the risk of falling victim to identity theft, financial loss, and other cybercrimes.
Here are some key tips to help you create strong passwords that will keep your accounts secure:
- Use Complex Passwords: Create passwords that are at least 12 characters long and include a mix of letters, numbers, and symbols.
- Avoid Common Passwords: Stay away from easily guessable passwords like “password123” or “123456.”
- Use a Phrase or Sentence: Consider a memorable phrase, like “MyD0gL0ves2PlayFetch!” (substituting some letters with numbers).
- Use a Password Manager as a Backup: If an account doesn’t yet support passkeys, a reputable password manager is still far safer than reusing or memorizing passwords. Treat it as a fallback, not your strongest option, and switch to a passkey as soon as one becomes available.
Strengthen Your Login Security: MFA and Passkeys
Multi-factor authentication (MFA) adds a second layer of proof that it’s really you logging in, but not all MFA methods are equally strong. Text-message codes and app push notifications can still be approved by mistake if you’re rushed or distracted. Passkeys are a newer, stronger alternative built to resist phishing and smishing entirely.
A passkey replaces your password with something you are or something you have, your fingerprint, your face, or your device’s screen lock, so there’s nothing for a scammer to steal by tricking you into typing it into a fake site. Whenever a service offers passkeys, consider these tips:
- Set up your passkey on your phone, not just in a browser. Storing a passkey using your phone’s built-in secure hardware (Face ID, fingerprint, or screen lock) is generally safer than relying only on a browser’s saved-password feature, since it’s tied to your physical device.
- Consider a hardware security key for your most important accounts. A physical key, such as a YubiKey, must be plugged in or tapped to log in, making remote takeover far more difficult, even for accounts like your Widener email or personal banking.
- Only set up a passkey when you initiate it yourself. Go directly to the account’s official app or website, never through a link someone sends you.
Learn more about how you can protect your privacy and security
Protecting Yourself from Social Engineering: Vishing, Smishing, and Beyond
Instead of hacking into computers or systems, social engineering attacks focus on how people think and trust others. Scammers often use tactics that play on emotions or create a sense of urgency to manipulate their targets.
Spotting Vishing and Smishing Scams
Two common methods of social engineering is vishing, where scammers target individuals through phone calls. Another tactic is smishing, which involves sending deceptive text messages. Because these methods come directly to your phone, they feel more personal, which can make you let your guard down. It’s important to recognize these tactics and know how to respond:
Vishing
- Don’t Share Personal Information: Never disclose personal details over the phone unless you can verify the caller’s identity.
- Verify the Caller: If you receive a suspicious call, hang up and call the organization directly using a number from their official website.
- Be Skeptical of Unsolicited Calls: Treat calls from unknown numbers cautiously, especially if they request sensitive information.
- Report Suspicious Calls: Mark vishing calls as Junk or Spam on your phone.
Smishing
- Don’t Click on Links in Unsolicited Texts: Be wary of messages from unknown numbers, especially those containing links.
- Verify the Sender: Contact the organization directly using a number from their official website if you receive a suspicious text.
- Don’t Share Personal Information: Never provide personal details in response to a text message.
- Use Security Features: Enable spam filters and antivirus software on your phone to help detect and block malicious messages.
A Growing Threat: AI-Powered Smishing and Social Engineering
Scammers are increasingly using AI tools to make vishing calls sound like a real, familiar person and to mass-produce convincing smishing texts that reference real events, like financial aid deadlines or package deliveries. Some newer scams also use QR codes in flyers or emails to send you to fake login pages, a tactic sometimes called “quishing.” The same rule applies no matter the format: if a message creates urgency and asks you to click, scan, call back, or “verify” something, stop and verify independently before you act.
Other Sneaky Social Engineering Tactics
Beyond vishing and smishing, it's important to recognize other social engineering tactics that scammers use:
- Pretexting: This involves scammers creating a fabricated scenario to steal your information by pretending to need it for a legitimate purpose.
- Baiting: Attackers may offer something enticing—like free downloads or promotions—to trick you into providing your personal information.
- Tailgating: This occurs when someone follows you into a secure area without proper authorization, often exploiting your trust or distraction.
Recognizing University Scams
At Widener University, we want to ensure that you can recognize potential scams and confidently safeguard your personal information, allowing you to have a secure academic experience. When you receive emails from Widener, remember that we will NEVER:
- Offer Jobs Requiring Upfront Payment: We won’t ask you to pay upfront for a job or request banking details.
Try to Sell You Used Goods: We do not sell used goods or offer discounted textbooks through email or text messages. - Ask You to Buy Gift Cards: We will never ask you to purchase gift cards in exchange for receiving money.
- Request Your Password or Sensitive Information: Widener University will NEVER ask you to verify or approve your account, share your password, Multi-Factor Authentication (MFA) PIN, or any other sensitive information via EMAIL, TEXT, or PHONE even if the message appears urgent or mentions a recent login.
- Ask You to Set Up or “Verify” a Passkey via a Link: Widener University will NEVER text you about your login, and will NEVER email you a link asking you to set up, register, re-verify, or confirm a passkey, security key, or biometric login. If a change to your account security is ever required, ITS will announce it well in advance, typically weeks or months of notice, never as an urgent demand to act immediately or lose access. Passkey enrollment should only ever be started by you, never through a link someone else sends you.
- Send Emails with “[EXTERNAL]” in the Subject: Emails with “[EXTERNAL]” indicate they are from outside sources, not from a Widener office.
If you have any doubts or need assistance, don’t hesitate to reach out to our Client Experience (CX) team for help by submitting a quick ticket, visiting the ITS resource website or Privacy & Security information page, or calling 610-499-1047.
By following these guidelines, you can help protect yourself from online threats. Stay vigilant and informed, and remember that your personal information is valuable—keep it safe! The more aware you are of potential scams and how to avoid them, the better equipped you’ll be to navigate your online environment securely. Stay safe!
Chris Smith serves as the Associate Vice President of IT Infrastructure at Widener University, where he plays a pivotal role in shaping and enhancing the university's technological framework. With a deep passion for cybersecurity, Chris is dedicated to ensuring the safety and integrity of the university's digital resources. He leads initiatives that focus on robust security measures, fostering a culture of awareness and vigilance across campus.